Data protection controls that are inconsistent across services
Encryption at rest and in transit is an AWS security objective that is easy to confirm for some services and easy to miss for others.
Encryption is not always enabled by default, and once initial setup is complete, most teams never revisit it as the environment expands. The AWS security assessment process checks the encryption status across data storage and transit configurations, alongside key management practices in AWS KMS, and produces a consolidated view of what is protected and where coverage ends.
IT experts are ready to start auditing AWS security for you
Certified AWS Partner delivering secure, scalable cloud-native solutions.
ISO-compliant processes ensuring quality, security, and reliability.
Trusted integration partner for financial data connectivity and open banking.
Team of ISTQB-certified QA engineers for world-class software testing.
Consistently rated ★5.0 by clients for reliability and delivery excellence.
Accredited partnership supporting advanced testing and continuous QA automation.
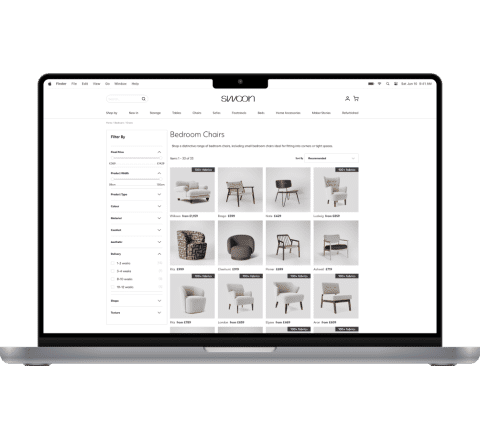
Swoon: Cloud-native backend for a furniture brand
Swoon partnered with Geniusee to modernize its backend and support a fast-growing e-commerce operation. The new serverless architecture cuts infrastructure costs, automates key workflows, and integrates payments, freight, and shipping systems into a single, reliable backbone for the brand.
Case details
How we secured a business-critical Atlassian platform with near-zero downtime by migrating VMware to AWS
We migrated a multi‑node Atlassian platform from a single VMware host to a resilient AWS architecture in a way that was almost invisible to end users. The client eliminated a single point of failure, strengthened their security posture, and gained a clear roadmap for further cloud modernization. Instead of relying on one aging server, they now run in AWS in the eu‑central‑1 region, with an environment ready for future load and security stability.
Case details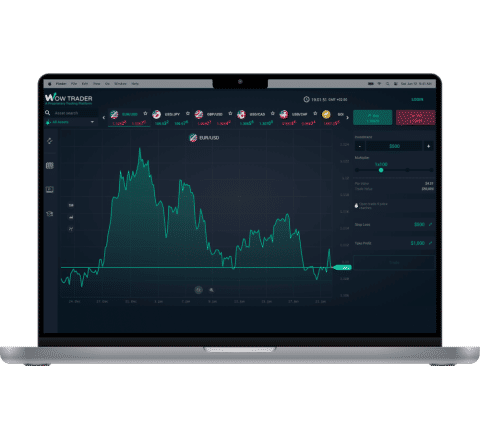
AWS Migration for TradeSmarter Trading Platform
Tradesmarter partnered with Geniusee to stabilize its trading infrastructure, enhance performance, ensure high availability, and automate processes – all while transitioning to a scalable cloud environment.
Case details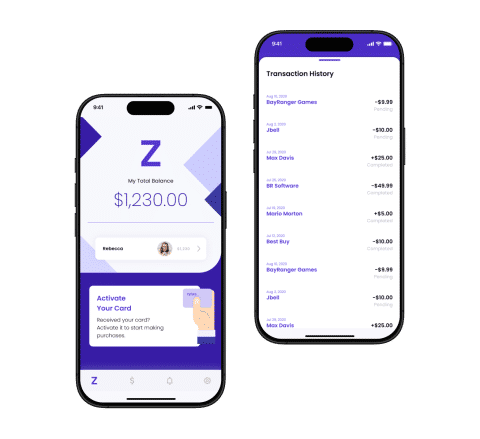
Zytara: Gamified digital banking app
Zytara is a digital banking app built specifically for Gen Z, combining financial education with a gamified, customizable user experience. Our team developed a secure, blockchain-enabled platform that lets parents manage and monitor their children’s spending and saving, while giving young users a more engaging way to interact with money. We introduced game-inspired card skins, personalized modes, and a built-in shop featuring branded merchandise from e-sports, gaming, and music partners. One of the most unique aspects of the project was enabling users to manage digital assets and complete full NFT lifecycles directly within the app.
Case details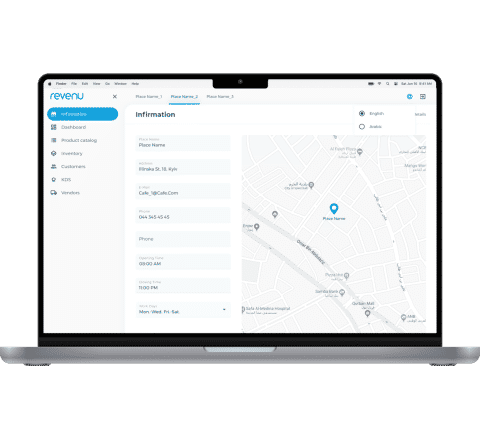
Revenu: All-in-one POS and restaurant management system
When Revenu approached Geniusee, they had a clear vision: to transform the restaurant experience through a unified POS and management system. Together, we set out to create a solution that simplifies restaurant operations, boosts staff efficiency, and enhances customer satisfaction.
Case details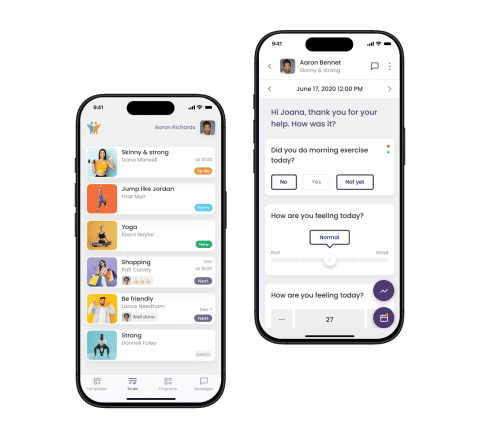
 Healthcare
Zebulon: Medtech app development
Zebulon set out to replace scattered health data with structured insight. The team wanted a mobile app that let clinicians build their own surveys, collect recurring inputs, and instantly see trends in a clear analytical view. With only the vision defined, Zebulon partnered with Geniusee to turn it into a functioning product. Our joint work resulted in a lightweight, secure application that captures continuous patient metrics and translates them into meaningful feedback for healthcare professionals.
Case details

Scope definition and access setup
The assessment begins with a scoping session where we define the AWS accounts, regions, and services in scope, agree on the assessment objectives and compliance frameworks relevant to your environment, and establish the access method. Configuration review is conducted using a read-only IAM role. The scope and boundaries of the penetration testing are agreed separately and confirmed before any active testing begins.
Automated discovery and manual configuration review
We run structured discovery across your AWS environment to collect the configuration state of IAM, networking, storage, encryption, and logging across all in-scope services. Automated collection is followed by manual review to identify patterns, context-specific risks, and findings that automated tools alone would not meaningfully interpret.
Risk analysis and finding prioritization
Collected configuration data is analyzed against AWS security best practices, CIS Foundations Benchmark controls, and the compliance requirements relevant to your organization. Each finding is assessed for severity based on the actual risk it introduces in your specific environment, not just whether it deviates from a default setting.
Report delivery and findings walkthrough
The assessment concludes with the delivery of a structured report that covers the executive summary, detailed findings, affected resources, and remediation guidance. We walk through the report with your technical team to answer questions, explain the context behind each finding, and help sequence the remediation work around your operational constraints.
Optional remediation support and verification
For teams that need engineering support to act on the findings, Geniusee can continue as a delivery partner through the remediation phase. This includes implementing the recommended configuration changes, confirming that fixes landed correctly, and running a follow-up review to close out the identified findings.
Optimize
Cloud work does not end when the system is running on AWS. We review usage, costs, incidents, performance data, and new business needs, then improve the environment through a continuous optimization loop.
AWS Advanced Tier Services Partner with established cloud delivery credentials
Geniusee is an AWS Advanced Tier Services Partner with DevOps and Education competencies, ISO 9001 and ISO 27001 certification, and a cloud engineering team active since 2017. The team conducting your assessment has hands-on experience configuring, migrating, and supporting AWS environments across FinTech, EdTech, Retail, and enterprise clients, which means every finding gets read through the lens of how infrastructure actually behaves in production.
Security that connects to how your product is actually built
Geniusee treats cybersecurity services as part of engineering delivery rather than a separate advisory track. During the assessment, findings are reviewed in the context of your infrastructure and your product’s operation. The result is recommendations your engineers can implement without creating new problems, rather than a report that names issues in isolation from how your environment actually works.
Evidence from live AWS engagements
Geniusee’s AWS work includes infrastructure migrations, long-term DevOps support, and AWS well-architected reviews across regulated and high-load environments. For a global FinTech trading platform, the team migrated the full infrastructure to AWS and established centralized monitoring and 24/7 L2 support. For an enterprise client, Geniusee handled a full VMware-to-AWS migration, reconfiguring IAM policies, security groups, and compliance controls without compromising data integrity.

A methodology your compliance team can reference, not just your engineers
The assessment follows a structured methodology that covers IAM, network exposure, data protection, and logging consistently across every engagement. Findings are documented in a format that engineering teams can act on and compliance teams can present during audits. Scope, access method, and report structure are agreed at the start, so there are no surprises about what the process covers or what it delivers.
ISO 27001 certification and QA maturity
Geniusee holds ISO 27001 certification, which means security controls are part of how the team operates day to day, not just what it delivers. The same standards applied internally carry into every assessment engagement.

- Security assessment for trading platforms, banking APIs, and payment processing infrastructure running on AWS
- IAM and network review for environments subject to PCI DSS, SOC 2, or financial services regulatory requirements
- Encryption and key management assessment for systems handling sensitive financial and transaction data
- Post-migration security review following AWS infrastructure consolidation for fintech platforms
- Logging and audit trail coverage review for environments requiring transaction-level traceability
- Security posture review for learning management systems and student data platforms operating on AWS
- FERPA and data protection alignment assessment for EdTech environments handling learner records
- S3 and content storage access control review for platforms serving course materials to large learner populations
- Network exposure review for platforms with high-volume concurrent user activity during peak periods
- Assessment preparation for enterprise EdTech clients entering procurement processes with large institutions
- Security assessment for eCommerce backends, POS systems, and order management platforms on AWS
- PCI DSS alignment review for retail environments processing card payments through AWS infrastructure
- Third-party integration and API access control review for platforms connected to payment, logistics, and CRM systems
- Data protection assessment for environments handling customer purchase history and behavioral data
- Serverless and containerized workload security review for AWS Lambda and ECS-based retail backends
- Security review for property management, listing, and CRM platforms running on AWS
- Access control assessment for platforms handling documents, contracts, and sensitive client information
- IAM and role separation review for multi-tenant platforms serving agents, landlords, investors, and buyers
- Data residency and encryption review for real estate platforms operating across multiple regions
- Security baseline documentation for real estate technology platforms entering enterprise or institutional sales
What is the purpose of an AWS security assessment?
An AWS security assessment provides your organization with a documented, prioritized view of security gaps and misconfigurations in your AWS environment. The goal is to identify risks before they become incidents, support compliance requirements that call for formal security documentation, and provide your engineering team with clear guidance on what to fix and in what order. It is particularly useful before compliance audits, enterprise sales cycles, infrastructure migrations, or whenever your AWS environment has grown significantly since it was last reviewed.
What does the AWS security assessment process involve?
The process covers scope definition, read-only access setup, automated configuration discovery across IAM, networking, storage, encryption, and logging, manual analysis to interpret findings in the context of your environment, and delivery of a structured report with prioritized recommendations. The configuration review does not modify your infrastructure. If penetration testing is included, active testing is separately scoped, approved, and conducted within agreed AWS policy boundaries, with findings folded into the same report.
What are the typical objectives of an AWS security assessment?
AWS security assessment objectives typically include identifying overprivileged IAM roles and unused credentials, locating publicly accessible resources that should be restricted, confirming encryption coverage across data storage and transit, verifying that logging is complete enough for security event detection and compliance, and documenting configuration gaps against frameworks such as SOC 2, ISO 27001, PCI DSS, or CIS AWS Foundations Benchmark. The specific objectives are confirmed during the scoping stage based on your compliance context and business priorities.
How long does an AWS security assessment take?
The timeline depends on the number of AWS accounts, regions, and services in scope. A focused assessment covering a single account and region typically completes within one to two weeks from access setup to report delivery. Larger environments with multiple accounts, regions, or complex networking require more time for discovery and analysis. The exact timeline is confirmed during the scoping session.
What access does Geniusee need to conduct the assessment?
The configuration review runs on a read-only IAM role created in your AWS account with permissions scoped to the services under review. No write access is required, and nothing in your infrastructure is changed during the review phase. Where penetration testing is included, the access requirements and testing boundaries are defined and agreed upon separately before any active testing begins.
Can Geniusee also fix the issues identified during the assessment?
Yes. Geniusee offers remediation support as a continuation of the assessment. The team can implement the recommended configuration changes within your AWS environment, either working alongside your engineers or taking direct ownership of the remediation tasks. A follow-up verification review confirms that the identified findings have been properly closed. The remediation scope and timeline are agreed separately after the assessment findings are reviewed together.
Does the assessment cover multiple AWS accounts?
Yes. The assessment can cover multi-account environments, including AWS Organizations setups where workloads are spread across separate accounts for environment separation, business unit segmentation, or compliance isolation. Multi-account scope is defined during the scoping session, and access is established for each account included in the review.
How does an AWS security assessment differ from an AWS Well-Architected Review?
An AWS Well-Architected Review evaluates your architecture across six pillars: operational excellence, security, reliability, performance efficiency, cost optimization, and sustainability. It is a broad architecture review that treats security as one dimension among several. An AWS security assessment goes deeper into that security dimension, covering IAM configuration, network exposure, encryption, and logging in more detail than a well-architected review typically does. The two complement each other well and can be run together or in sequence.